Nobody likes cookie banners:
- As a visitor, they can feel like a frustrating hurdle between you and the content you came to see.
- As a WordPress or WooCommerce website owner, they can feel like a cost with no upsides.
And yet, depending on your website’s purpose, you may not need one at all.
If your website only uses cookies and similar technologies that are strictly necessary for the service you provide, you may be able to operate without a traditional “Accept All Cookies” banner.
That doesn’t mean you can ignore privacy law compliance. It means the better solution may be to design your website so that it doesn’t need consent for unnecessary tracking in the first place.
Here’s what cookies actually do, when consent may be required, and how you can reduce or eliminate unnecessary tracking on a WordPress or WooCommerce website.
Cookies are small pieces of data stored in a visitor’s browser by a website. They allow websites to remember information between page loads or visits.
For example, an online store might use cookies to remember:
- What’s in a visitor’s shopping cart.
- Whether a visitor is logged into their account.
- Certain preferences or settings.
- Which language or region they selected.
But not all cookies serve the same purpose.
For privacy, it’s useful to distinguish between strictly necessary technologies and non-essential tracking.
These are technologies that are necessary to provide a service the visitor has requested or to make the website function as intended.
On a WooCommerce store, examples can include cookies associated with shopping-cart functionality, customer sessions, checkout processes, and authentication.
Depending on the applicable law and how the technology is used, these may not require the same type of consent as advertising or analytics cookies.
These technologies and cookies can help with analytics, advertising, profiling, personalization, or cross-site tracking.
Examples can include:
- Advertising pixels.
- Certain Google Analytics configurations.
- Meta Pixel.
- Third-party advertising scripts.
- Some embedded video, map, and social-media content.
These are cases when privacy laws require a website owner to acquire user consent before using these technologies and cookies. What is the best or default way to acquire this consent? Exactly! Cookie banners!
You don’t necessarily need a cookie banner simply because your website uses cookies.
The important questions to figure out whether you even need a cookie banner:
- What technologies does your website use?
- What information do they collect?
- Why is that information being collected?
- Which laws apply to your visitors?
- Does the particular processing require consent?
If your website can function without non-essential tracking, removing those trackers may be a much better solution than adding another intrusive banner.
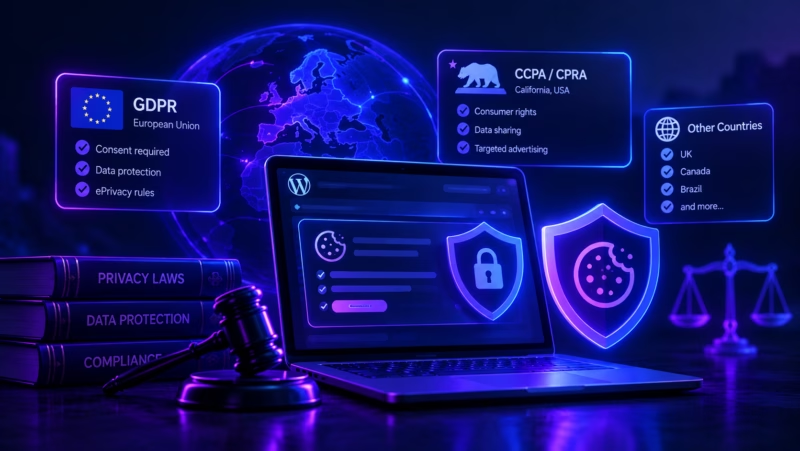
Why You Need to Care About Cookie and Privacy Laws?
Cookie compliance isn’t only an issue for large corporations.
Small businesses, freelancers, publishers, and online stores can also have obligations under privacy and electronic communications laws.
The exact requirements depend on where your visitors are located and what your website does.
For websites serving people in the European Economic Area, the GDPR and ePrivacy rules apply.
- In general, storing or accessing information on a user’s device for purposes that aren’t strictly necessary can trigger consent requirements.
- When consent is required, your website has to acquire it before the relevant processing begins.
- Consent has to meet specific requirements. For example, simply hiding an “Accept” button behind a confusing interface isn’t enough.
California’s CCPA/CPRA rules apply to your website if you are serving content/services to users in that USA state. This law takes a different approach than the previously mentioned laws.
- Among other things, it gives California consumers rights concerning the sale or sharing of personal information and certain forms of targeted advertising.
- That means a cookie banner isn’t automatically the answer to every U.S. privacy issue. Your website needs to consider what information it collects and how that information is used or disclosed.
Other jurisdictions have their own privacy and electronic-communications requirements, including the UK, Canada, Brazil, and many others.
So rather than assuming that one cookie-banner configuration makes a website “globally compliant,” it’s better to identify the jurisdictions that matter to your business and audit the technologies your website actually uses.
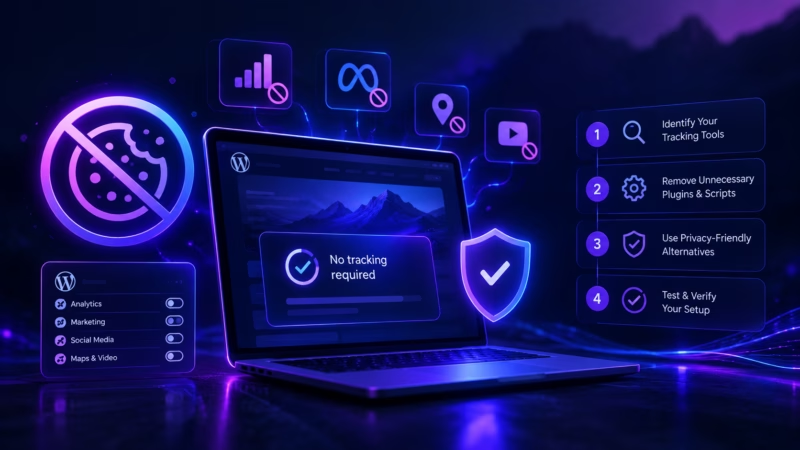
How to Reduce Tracking and Potentially Ditch the Cookie Banner?
If your goal is to remove a cookie banner, the first step isn’t installing a different banner plugin.
The first step is removing the technologies that require consent in the first place.
Here are some practical ways to do that.
Analytics is one of the most common reasons websites introduce non-essential tracking.
Traditional analytics platforms can use cookies, identifiers, and other technologies to understand visitor behavior. Whether a particular configuration requires consent depends on the platform, configuration, jurisdiction, and processing involved.
A standard example is Google Analytics, which can track every action a user takes on your website. From who they are and what device they use to the specific services they purchase. This information is then sent to Google. Because this tracking is not strictly necessary for your website to function, and because a third party may use this data in ways the user never intended, you must acquire explicit consent before collecting and sharing it.
We can use analytics platforms designed to minimize personal data collection and, in some configurations, operate without cookies.
Some technologies that can be used to achieve this include:
- Matomo, when appropriately configured.
- Independent Analytics plugin.
Yet, don’t assume that installing an analytics platform automatically exempts your website from consent requirements.
The goal is to collect the information you genuinely need – page views, referral sources, and conversions – without unnecessarily identifying or tracking individual visitors.
Third-party embeds are another common source of unwanted tracking.
A YouTube video, Google Maps widget, social-media embed, or other third-party component may make requests to an external service as soon as the page loads.
That can introduce privacy implications before the visitor has actively interacted with the content.
Instead of loading the third-party service immediately, you can display a placeholder.
For example:
“This video is hosted by YouTube. Click the button above to load the video and connect to YouTube.”
Third-party content loads only after the visitor clicks the button.
This approach is often called a two-click solution, content blocker, or facade.
It can provide a much better user experience than displaying a large cookie banner across the entire website just because one page contains a YouTube video.
However, the exact wording and implementation should match the legal requirements that apply to your website.
Consent doesn’t always mean adding a website-wide cookie banner.
Sometimes the better solution is to prevent a non-essential third-party service from loading until the visitor actively requests it.
Third-party resources can create privacy considerations that website owners sometimes overlook.
A common example is loading fonts directly from an external provider rather than hosting them on your own server.
When a visitor’s browser requests a resource from a third-party server, information such as the visitor’s IP address can potentially be disclosed to that provider.
This has already resulted in legal disputes in Europe, including cases involving externally hosted fonts. For example, the 2022 Munich court case involving Google Fonts.
Instead of requesting fonts and other static resources from third-party services, you can often host them directly on your own infrastructure.
Benefits:
- Reduce third-party requests.
- Gives you more control over what information leaves your website.
- Reduce dependencies on external services.
- Sometimes improve performance.
The same principle can be applied to other externally loaded resources where practical.
This is one of the most important – and most frequently overlooked – steps.
You may think your website is “cookie-free” because you removed Google Analytics, while a WordPress plugin is quietly loading:
- Advertising scripts.
- Social-media pixels.
- Analytics services.
- Chat widgets.
- Heatmaps.
- A/B testing tools.
- External fonts.
- Third-party embeds.
Your website’s privacy configuration is determined by what the website actually does – not by what you think you installed.
A proper audit should therefore note network requests and storage mechanisms, ideally across important pages such as the homepage, product pages, cart, checkout, and account area.
Potentially, yes.
A basic WooCommerce store needs cookies and other mechanisms for essential functions such as maintaining shopping-cart and customer-session functionality.
Those necessary technologies aren’t automatically advertising or cross-site tracking cookies.
However, a real WooCommerce installation rarely exists in isolation.
Your payment provider, analytics platform, marketing tools, chat software, advertising pixels, embedded content, and other plugins may introduce additional processing.
So instead of asking:
“Does WooCommerce require a cookie banner?”
The more useful question is:
“What does my website actually load, store, and transmit?”
That is what needs to be audited.
This article is for informational purposes only and does not constitute legal advice. Please consult a qualified legal professional to ensure your store's specific operations comply with local and/or international regulations.